Risk register
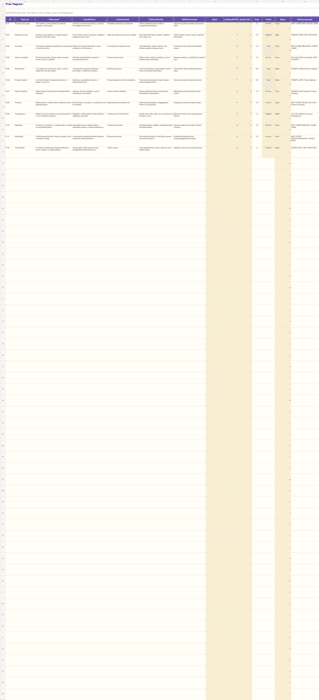
Twelve starter risk areas with failure modes, harms, mitigations, evidence, owners, scoring, status, and reference prompts.
A practical operating kit for teams that need to identify risks, plan evaluations, check which frameworks and regulations may apply, collect evidence, and make an accountable launch decision.
These selected previews show the workbook structure and the field guide included in the download. Detailed rows, formulas, templates, and guidance remain in the paid kit.
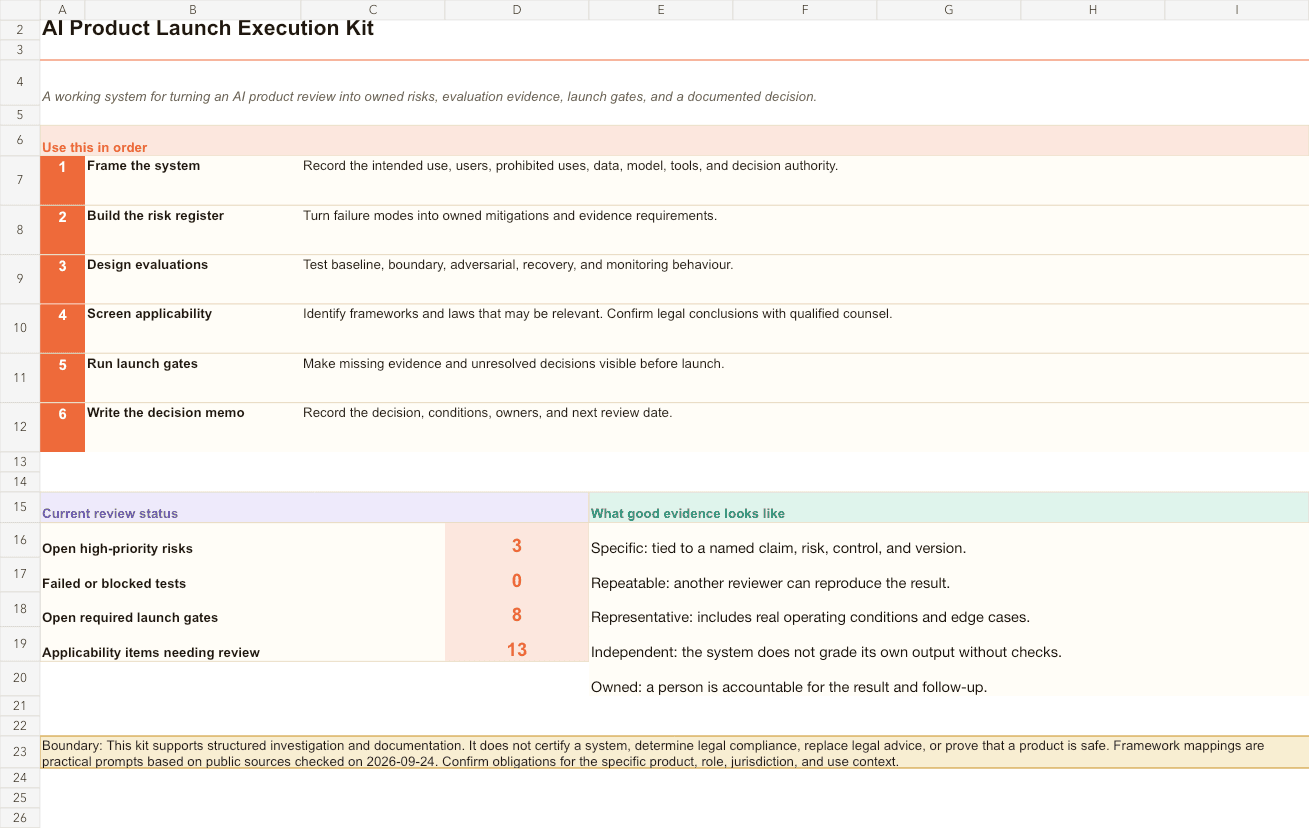 Selected preview
 Selected preview
Editable workbook
Starter risks with scoring, mitigations, evidence requirements, owners, and framework prompts.
 Selected preview
Editable workbook
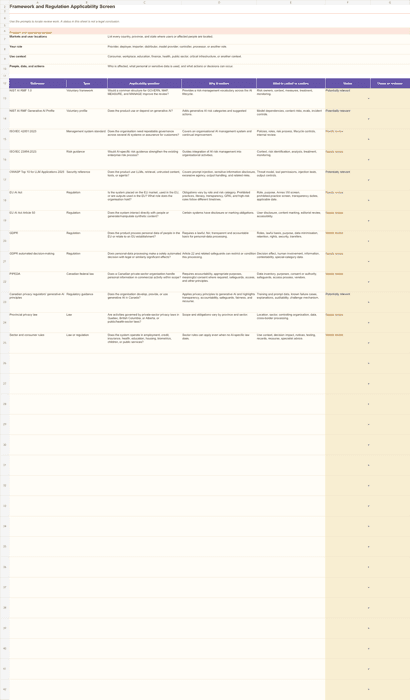
Fact-based prompts for frameworks, security references, regulations, privacy laws, and sector review.
 Selected preview
11-page field guide
Plain-language instructions, evidence standards, framework mapping, and a worked example.
The free review makes the first questions visible. The paid kit gives you editable artifacts for owners, evidence, decisions, and follow-through.
Twelve starter risk areas with failure modes, harms, mitigations, evidence, owners, scoring, status, and reference prompts.
Baseline, boundary, adversarial, recovery, oversight, fairness, regression, and monitoring tests with thresholds and evidence fields.
Trigger questions for NIST, ISO, OWASP, the EU AI Act, GDPR, PIPEDA, Canadian privacy guidance, and sector rules.
Required evidence and owner fields for product scope, data, security, oversight, legal review, monitoring, and the final decision.
A decision memo, 45-minute review agenda, conditions log, monitoring plan, and explicit next-review triggers.
An 11-page method with worked examples, evidence standards, a framework crosswalk, and links to official sources.
The kit separates voluntary frameworks, security references, laws, and regulatory guidance. It records the product facts that determine applicability and leaves the legal conclusion with a qualified reviewer.
GOVERN, MAP, MEASURE, and MANAGE across the review lifecycle.
Generative AI risks and suggested actions.
AI management systems and organisational governance.
AI-specific risk management guidance.
Application security risks such as prompt injection and excessive agency.
Role, market, data, decision impact, transparency, privacy, and sector review questions.
The kit supports investigation and documentation. It does not inspect your product, certify a system, determine legal compliance, replace legal advice, or prove that a product is safe. The workbook makes those boundaries visible rather than hiding them.
Get the kit — CA$39